Application Programming Interface Security Market
Application Programming Interface Security Market Size, Scope, Growth, Trends and By Segmentation Types, Applications, Regional Analysis and Industry Forecast (2026-2034)
Report ID : RI_711279 | Published On : October 24, 2026 |
Format : 


 | Author : Vigneshwaran Mahadik
Application Programming Interface Security Market Size
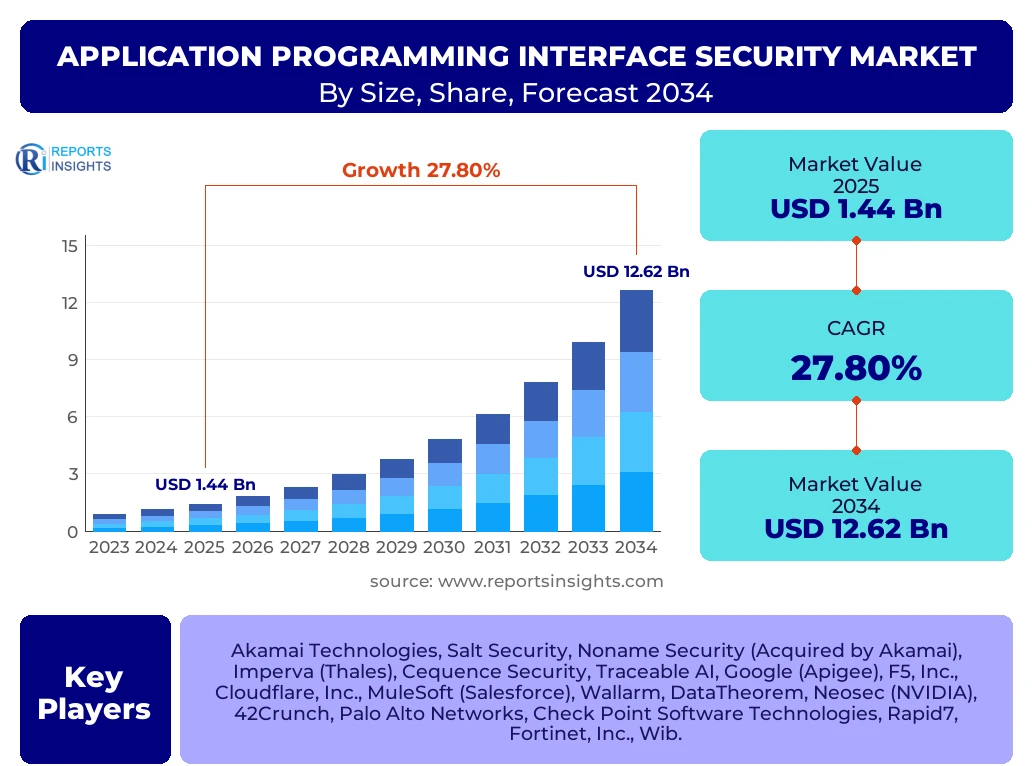
According to Reports Insights Consulting Pvt Ltd, The Application Programming Interface Security Market is projected to grow at a Compound Annual Growth Rate (CAGR) of 27.8% between 2025 and 2034. The market is estimated at USD 1.84 Billion in 2026 and is projected to reach USD 12.62 Billion by the end of the forecast period in 2034.
Key Application Programming Interface Security Market Trends & Insights
The Application Programming Interface (API) security market is undergoing a fundamental transformation as organizations transition from traditional monolithic architectures to microservices and cloud-native environments. A critical trend is the shift-left security approach, where security testing is integrated directly into the Continuous Integration and Continuous Deployment (CI/CD) pipeline. This allows developers to identify vulnerabilities such as Broken Object Level Authorization (BOLA) and insecure endpoints during the coding phase rather than post-production. Furthermore, the integration of Artificial Intelligence and Machine Learning is becoming standard for behavioral baseline analysis, enabling the detection of sophisticated, low-and-slow attacks that bypass traditional signature-based Web Application Firewalls (WAF).
- Largest Region: North America remains the dominant market due to the high concentration of technology enterprises, early adoption of zero-trust architectures, and stringent data protection regulations such as CCPA.
- Fastest Growing Region: Asia-Pacific is expected to witness the highest CAGR, fueled by rapid digitalization in emerging economies like India and Southeast Asia, and the massive expansion of fintech and e-commerce sectors.
- Largest Segment by Offering: The Platform segment holds the largest market share as enterprises prefer integrated solutions that provide discovery, posture management, and runtime protection in a single pane of glass.
- Dominant Deployment Mode: Cloud-based deployment leads the market, driven by the inherent scalability requirements of modern API ecosystems and the proliferation of SaaS-based business models.
Key Takeaways Application Programming Interface Security Market Size & Forecast
The rapid expansion of the API security market is primarily dictated by the exponential growth in API traffic, which now accounts for over 80% of all internet traffic. As businesses increasingly rely on APIs for internal communication and third-party integrations, the attack surface has expanded significantly. The market forecast indicates a robust shift toward dedicated API security tooling, as general-purpose security solutions are proving inadequate against API-specific threats defined in the OWASP API Security Top 10. Strategic investments are moving toward automated discovery tools to eliminate the risk of shadow and zombie APIs that often remain unmonitored and unprotected.
- BFSI Leadership: The Banking, Financial Services, and Insurance (BFSI) sector is the leading end-user vertical, mandated by Open Banking regulations and the need to secure highly sensitive financial data transactions.
- Rise of GraphQL: While REST remains the most common API type, the increasing adoption of GraphQL is creating new security requirements, specifically regarding deep query nesting and complex authorization checks.
- Regulatory Pressure: Global compliance frameworks like GDPR and PCI-DSS 4.0 are acting as major catalysts, forcing organizations to implement granular API logging and monitoring to avoid heavy non-compliance penalties.
- Focus on API Posture Management: There is a heightened focus on API Security Property Management (ASPM), which provides continuous visibility into the API inventory and helps in identifying misconfigurations before they are exploited.
Application Programming Interface Security Market Drivers Analysis
The primary driver for the market is the massive proliferation of mobile applications and IoT devices, both of which rely heavily on APIs for data exchange and functional interoperability. As organizations modernize their legacy systems into microservices, the number of internal and external APIs grows exponentially, creating a critical need for specialized security layers. Additionally, the increasing frequency and sophistication of API-related data breaches have moved API security from a technical requirement to a boardroom priority, accelerating budget allocations for advanced protection platforms.
| Drivers | (~) Impact on CAGR % Forecast | Regional/Country Relevance | Impact Time Period |
|---|---|---|---|
| Acceleration of Digital Transformation & Microservices | +8.5% | Global | 2025 - 2034 |
| Rising Frequency of BOLA and Injection Attacks | +6.2% | North America and Europe | 2025 - 2028 |
| Stringent Regulatory Compliance (PCI-DSS 4.0, GDPR) | +5.4% | European Union | 2025 - 2030 |
| Expansion of Open Banking Ecosystems | +4.7% | UK, Brazil, India | 2026 - 2034 |
Application Programming Interface Security Market Restraints Analysis
Despite high growth potential, the market faces significant restraints, including a critical shortage of cybersecurity professionals who understand the nuances of API logic and development. Furthermore, the complexity of integrating API security tools within legacy IT infrastructures can lead to performance latency, which often discourages organizations from implementing comprehensive deep-packet inspection. High initial costs of premium API security platforms also pose a barrier for Small and Medium-sized Enterprises (SMEs) that operate on limited security budgets.
| Restraints | (~) Impact on CAGR % Forecast | Regional/Country Relevance | Impact Time Period |
|---|---|---|---|
| Cybersecurity Skill Gap & Specialized API Knowledge | -3.2% | Global | 2025 - 2034 |
| High Implementation Costs for Specialized Tooling | -2.8% | Emerging Markets (APAC/LATAM) | 2025 - 2029 |
| Performance Latency and False Positives | -1.5% | Global | 2025 - 2034 |
Application Programming Interface Security Market Opportunities Analysis
Significant opportunities lie in the development of AI-driven autonomous API discovery and cataloging tools that can identify shadow APIs without manual intervention. The integration of API security with Service Mesh architectures offers a massive growth avenue for vendors to provide security at the sidecar level. Moreover, the growth of the "API economy" in the healthcare sector, driven by interoperability standards like FHIR, presents a specialized niche for security providers to offer HIPAA-compliant API protection solutions.
| Opportunities | (~) Impact on CAGR % Forecast | Regional/Country Relevance | Impact Time Period |
|---|---|---|---|
| AI-Powered Threat Hunting and Behavior Analysis | +7.8% | United States, Israel, Germany | 2026 - 2034 |
| Healthcare Data Interoperability (FHIR Standards) | +5.1% | North America | 2025 - 2032 |
| API Security for Serverless Architectures | +4.3% | Global | 2027 - 2034 |
Application Programming Interface Security Market Challenges Impact Analysis
The dynamic nature of API development, where updates are pushed multiple times a day, creates a major challenge for maintaining consistent security postures. Traditional security methods cannot keep pace with the velocity of DevOps, leading to "protection gaps" between releases. Additionally, the rise of sophisticated automated bot attacks that mimic legitimate user behavior through APIs makes it increasingly difficult to differentiate between high-value customer traffic and malicious scraping or account takeover attempts.
| Challenges | (~) Impact on CAGR % Forecast | Regional/Country Relevance | Impact Time Period |
|---|---|---|---|
| Discovery of Shadow and Zombie APIs | -4.1% | Global | 2025 - 2034 |
| Sophisticated Bot Attacks on Public Endpoints | -3.5% | China, USA, Russia | 2025 - 2030 |
| Ensuring Security in Multi-Cloud Environments | -2.2% | Global | 2025 - 2034 |
Application Programming Interface Security Market - Updated Report Scope
This report provides an in-depth analysis of the global Application Programming Interface Security market, covering historical data from 2020 to 2024 and providing a comprehensive forecast until 2034. The scope includes a detailed breakdown of offerings, deployment models, organization sizes, and industry verticals across six major geographic regions. The analysis focuses on the technological convergence of WAF, WAAP, and dedicated API security platforms, while evaluating the impact of emerging threats like AI-generated malicious scripts on the overall market dynamics.
| Report Attributes | Report Details |
|---|---|
| Base Year | 2025 |
| Historical Year | 2020 to 2024 |
| Forecast Year | 2026 - 2034 |
| Market Size in 2025 | USD 1.44 Billion |
| Market Forecast in 2034 | USD 12.62 Billion |
| Growth Rate | 27.8% CAGR |
| Number of Pages | 265 |
| Key Trends |
|
| Segments Covered |
|
| Key Companies Covered | Akamai Technologies, Salt Security, Noname Security (Acquired by Akamai), Imperva (Thales), Cequence Security, Traceable AI, Google (Apigee), F5, Inc., Cloudflare, Inc., MuleSoft (Salesforce), Wallarm, DataTheorem, Neosec (NVIDIA), 42Crunch, Palo Alto Networks, Check Point Software Technologies, Rapid7, Fortinet, Inc., Wib. |
| Regions Covered | North America, Europe, Asia Pacific (APAC), Latin America, Middle East, and Africa (MEA) |
| Speak to Analyst | Avail customised purchase options to meet your exact research needs. Request For Analyst Or Customization |
Segmentation Analysis
The Application Programming Interface Security market is segmented based on offering, deployment mode, organization size, and industry vertical. The platform segment is currently the largest, as it provides comprehensive capabilities such as API discovery, vulnerability management, and runtime protection. Cloud-based deployment is the preferred choice for modern enterprises due to its agility and lower overhead costs. Among industry verticals, the BFSI sector remains the primary revenue contributor, driven by high security requirements for digital payments and mobile banking. The SME segment is expected to show high growth as cost-effective, automated security solutions become more widely available in the market.
- By Offering:
- Platforms (API Discovery, Posture Management, Threat Protection)
- Services (Professional Services, Managed Security Services)
- By Deployment Mode:
- Cloud-Based
- On-Premises
- Hybrid
- By Organization Size:
- Large Enterprises
- Small and Medium-sized Enterprises (SMEs)
- By API Type:
- REST (Representational State Transfer)
- SOAP (Simple Object Access Protocol)
- GraphQL
- By Industry Vertical:
- Banking, Financial Services, and Insurance (BFSI)
- IT and Telecommunications
- Healthcare and Life Sciences
- Retail and E-commerce
- Government and Defense
- Manufacturing
- Media and Entertainment
Regional Highlights
- North America: This region accounts for the largest market share, approximately 38%, driven by early technological adoption and the presence of major industry players like Akamai, F5, and Google. The US is the central hub for API security innovation.
- Europe: Europe is the second-largest market, with a strong focus on data privacy and compliance. Germany and the UK are leading adopters, primarily influenced by GDPR and Open Banking regulations.
- Asia-Pacific: This is the fastest-growing region, expected to expand at a CAGR of over 31% through 2034. Rapid cloud migration in India, China, and Japan is creating a massive demand for secure API frameworks.
- Latin America: Growth is primarily seen in Brazil and Mexico, where the fintech sector is booming and digital payment infrastructure is being modernized.
- Middle East & Africa: Adoption is increasing in the GCC countries as they invest heavily in smart city initiatives and digital government services, requiring robust API security layers.

Top Key Players
The market research report includes a detailed profile of leading top wise companies in the Application Programming Interface Security Market.- Akamai Technologies
- Salt Security
- Noname Security
- Imperva (Thales Group)
- Cequence Security
- Traceable AI
- Google Cloud (Apigee)
- F5, Inc.
- Cloudflare, Inc.
- MuleSoft (Salesforce)
- Wallarm
- DataTheorem
- Neosec (NVIDIA)
- 42Crunch
- Palo Alto Networks
- Check Point Software Technologies
- Rapid7
- Fortinet, Inc.
- Wib
- AppCheck Ltd.
Frequently Asked Questions
What is the current market size of the global API Security market?
As of 2025, the market is valued at approximately USD 1.44 Billion and is projected to experience rapid growth reaching over USD 12 Billion by 2034, driven by the expansion of the API economy.
Which industry vertical is the largest user of API security solutions?
The BFSI (Banking, Financial Services, and Insurance) sector is the largest end-user, necessitated by high-security requirements for financial transactions, regulatory compliance, and the growth of Open Banking.
What are the main threats that API security platforms address?
API security platforms primarily target the OWASP API Security Top 10 threats, including Broken Object Level Authorization (BOLA), Broken User Authentication, Excessive Data Exposure, and Lack of Resources & Rate Limiting.
What is the difference between a WAF and a dedicated API security platform?
A traditional WAF uses signature-based detection for known web threats, whereas a dedicated API security platform uses behavioral analysis to understand API logic, discover hidden endpoints, and prevent attacks that look like legitimate traffic.
How does the "Shift-Left" approach impact the API security market?
Shift-left security encourages the integration of API testing early in the development lifecycle. This trend is driving demand for automated tools that integrate with developer IDEs and CI/CD pipelines to catch vulnerabilities before deployment.
Author
V
Vigneshwaran Mahadik is a Senior Analyst IT and Telecommunications Research with over 6+ years of experience in the IT and Telecommunications Industry. He specializes in technology market intelligence, digital transformation analysis, cloud computing trends, telecom infrastructure assessment, competitive benchmarking, market sizing, demand forecasting, and emerging technology evaluation across enterprise and communication ecosystems. His research combines comprehensive industry analysis with data-driven methodologies to help organizations make strategic business decisions, identify new growth opportunities, optimize operational strategies, anticipate evolving market trends, and strengthen their competitive positioning in the global IT and telecommunications landscape.
| Single User | : $3680 |
|---|---|
| Multi User | : $5680 |
| Corporate User | : $6400 |
Buy Now
Secure SSL Encrypted
